42Crunch Platform release, November 5, 2026
|
Platform version: v1.61.x |
This 42Crunch API Security Platform release brings custom scalars for GraphQL and improves the support for OpenAPI Specification (OAS) v3.1.x.
New features
The following are the new features and improvements to the existing ones in this release.
Improvements to the OAS v3.1.x support in API Security Audit
All keywords from JSON Schema Draft 2020-12, such as patternProperties, are now correctly recognized as accepted properties in the OAS v3.1.x.
We have also implemented a new check to catch APIs that define webhooks but no paths. Such APIs cannot be scanned with API Scan: webhooks send data when a pre-defined event occurs, while API Scan requires an endpoint that it can send a request to. Because API Scan cannot call a webhook endpoint directly, an API with only webhooks exposes no endpoint that API Scan could use. While such APIs are valid as per the OAS v3.1.x, this check may help you to understand why API Scan cannot run a scan on it. For more details, see API definition declares webhooks but no paths.
Improvements to GraphQL support
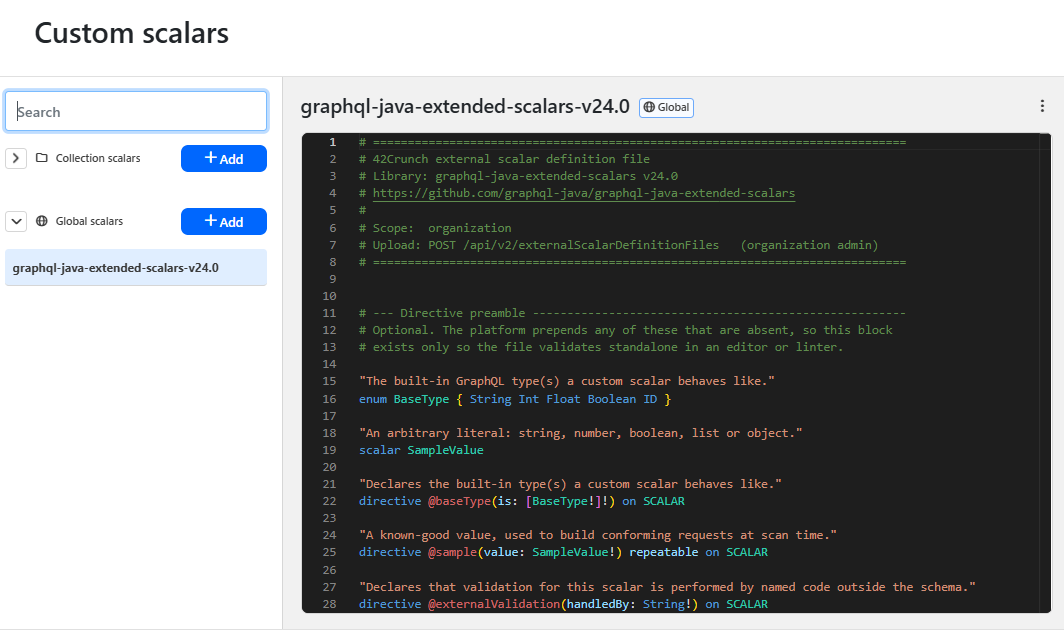
You can now define reusable custom scalar libraries that allow centralizing custom scalars and their governance. The custom scalars are defined using the standard GraphQL schema definition language in a separate file that is uploaded to the platform. Security Audit and API Scan automatically take into account any custom scalar files that they find, with no additional changes required to the GraphQL API definitions themselves: simply using such a custom scalar in the API definition is enough.
Custom scalars can be managed as part of the API collections where the APIs that use them reside, by the teams working on those APIs. Or they can be a global organization-level resource used by all GraphQL APIs in the organization and managed by organization administrators. For more details on custom scalars and how they can be used, see Custom scalar libraries.
Scan customization rules now let you define how long error responses can be before API Scan should consider them excessive. By default, error messages can be 1000 characters long, but extending the limit further may be useful if longer messages are required, for example, to advise downstream services. For more details, see Scan customizations for GraphQL APIs.
In addition, we have adjusted the scoring algorithm for GraphQL data definition files. Previously, the score might vary unpredictably from audit to another even when the found issues stayed the same. This was because the order in which Security Audit traversed through the arguments in a GraphQL API might vary between the audits and could affect how the algorithm calculated the score, leading to the same API getting different scores without any change to the API itself. Now, the order in which Security Audit traverses the API definition no longer has an impact on how the audit score for data definition files is calculated.
We have also fixed the following:
- Security Audit now correctly recognizes directives like
@liston the arguments of interface-owned fields. - Unresolved variables (
%s) in the descriptions in the audit report are now correctly populated. - API Scan now correctly restricts the values it generates built-in
Intscalars to 32-bit range, as per the GraphQL specification.
Support for GraphQL is not enabled by default, but is available as a separate subscription. If you are interested in adding GraphQL support to your subscription, contact sales@42crunch.com.
GraphQL is not yet supported in API Protection, CI/CD plugins, or data dictionaries.
Improvements to API Scan
Operations that have been skipped from the scan either through scan customization rules or in the scan configuration itself are now excluded when calculating the coverage in scan security quality gates (SQGs). This allows APIs where some operations were legitimately not scanned to pass a scan SQG imposing strict coverage criteria. We have also improved how skipped tests are indicated in the scan report. For more details, see Security quality gates.
42Crunch Platform now correctly returns HTTP 404 when a scan report is not found, instead of the previous HTTP 403.
Improvements to parsing API definitions
Previously, very large API definitions where the file size was close but still under the 10 MB limit might have been deemed too large. This was because the whitespace formatting that made the file more human-readable was included in the file stored in the platform, which could significantly increase the size of the stored file, especially with complex or deeply nested API definitions. Now, such API definitions are stored as a string without the whitespace to keep the size of the stored file smaller.
We have also improved how numbers starting with a leading 0 are parsed in YAML. Previously, a number expressed as 007 was parsed as is, which could cause problems with the numeric checks in Security Audit. Now, 007 is correctly parsed as 7.
Compatibility
This section lists the compatible Docker images for some of the components of 42Crunch API Security Platform, as well as other possible compatibility details.
API Firewall images
This release is compatible with the following API Firewall images:
- NEW:
42crunch/apifirewall:v1.2.13- Performance optimizations
- Upgrade to
go-1.27.3(CVE-2026-111943) - Upgrade to
golang.org/x/net v0.62.0(CVE-2026-78661, CVE-2026-97045) - Upgrade to
Alpine 3.24.3:libexpat 2.9.0(CVE-2026-77214, CVE-2026-102633)musl 1.2.6-r3(CVE-2026-107891)
We highly recommend that you switch to the latest image version to take full advantage of the new features and security improvements.
42crunch/apifirewall:v1.2.12- Raise GRPC message limit in API Firewall to 128 MB when fetching protection configuration
- Upgrade to
go-1.27.2(CVE-2026-97032, CVE-2026-78667, CVE-2026-78659, CVE-2026-97031, CVE-2026-94439, CVE-2026-78663, CVE-2026-78669, CVE-2026-94440, CVE-2026-56866, CVE-2026-56857, CVE-2026-78659, CVE-2026-78660, CVE-2026-78663, CVE-2026-78669, CVE-2026-97032, CVE-2026-102633)
42crunch/apifirewall:v1.2.11- Upgrade to
go-grpc-1.83.1(CVE-2026-84303, CVE-2026-84304, CVE-2026-84445) - Upgrade to
openssl-3.5.8CVE-2026-14456, CVE-2026-14457, CVE-2026-18798, CVE-2026-54874, CVE-2026-63072, CVE-2026-63073, CVE-2026-63074, CVE-2026-63075, CVE-2026-63076, CVE-2026-75803) - Upgrade to
util-linux 2.42.3(CVE-2026-76642, CVE-2026-78408, CVE-2026-78409, CVE-2026-78410) - Upgrade to
expat-2.8.4(CVE-2026-66046, CVE-2026-76641, CVE-2026-76956, CVE-2026-76957) - Upgrade to
pcre2-10.48(CVE-2026-89157, CVE-2026-89160, CVE-2026-89162)
- Upgrade to
42crunch/apifirewall:v1.2.10- Upgrade to
go-1.26.6(CVE-2026-33818, CVE-2026-56853, CVE-2026-56858, CVE-2026-56859, CVE-2026-56860, CVE-2026-56862, CVE-2026-56864, CVE-2026-568652) - Upgrade to
apr-util-1.6.5(CVE-2025-49506, CVE-2026-32327, CVE-2026-341) - Upgrade to
memcached-1.6.45(CVE-2026-47783, CVE-2026-47784)
- Upgrade to
42crunch/apifirewall:v1.2.9- Upgrade to
go-grpc-1.82.1(GHSA-hrxh-6v49-42gf) - Upgrade to
go-1.26.5(CVE-2026-39822) - Upgrade to
expat-2.8.2(CVE-2026-50219)
- Upgrade to
42crunch/apifirewall:v1.2.7- Upgrade to
openssl-3.5.7(CVE-2026-34180, CVE-2026-34181, CVE-2026-34182, CVE-2026-34183, CVE-2026-35188, CVE-2026-42764, CVE-2026-42765, CVE-2026-42766, CVE-2026-42767, CVE-2026-42768, CVE-2026-42769, CVE-2026-42770, CVE-2026-45445, CVE-2026-45446, CVE-2026-45447, CVE-2026-7383, CVE-2026-9076)
- Upgrade to
42crunch/apifirewall:v1.2.6- Fix loading some OpenAPI definitions that failed with an error on unresolved reference
- Upgrade to
httpd-2.4.68(CVE-2026-29167, CVE-2026-29170, CVE-2026-34355, CVE-2026-34356, CVE-2026-42535, CVE-2026-42536, CVE-2026-43951, CVE-2026-44119, CVE-2026-44185, CVE-2026-44186, CVE-2026-44631, CVE-2026-48913, CVE-2026-49975) - Upgrade to
golang-1.26.4(CVE-2026-27145, CVE-2026-42504, CVE-2026-42507) - Upgrade to
go-net v0.55.0(CVE-2026-39821)
42crunch/apifirewall:v1.2.4- Upgrade to
golang-1.26.3(CVE-2026-32283, CVE-2026-32282, CVE-2026-27144, CVE-2026-27140, CVE-2026-27143, CVE-2026-33810, CVE-2026-32289, CVE-2026-32288, CVE-2026-42501, CVE-2026-27142, CVE-2026-39836) - Upgrade to
openssl-3.5.6(CVE-2026-31789, CVE-2026-28387, CVE-2026-40200, CVE-2026-2673) - Upgrade to
httpd-2.4.67(CVE-2026-23918, CVE-2026-24072, CVE-2026-28780, CVE-2026-29168, CVE-2026-29169, CVE-2026-33006, CVE-2026-33007, CVE-2026-33523, CVE-2026-33857, CVE-2026-34032, CVE-2026-34059)
- Upgrade to
42crunch/apifirewall:v1.2.3- Upgrade to
go-1.26.1
- Upgrade to
-
42crunch/apifirewall:v1.2.2- Upgrade to
go-grpc 1.79.3(CVE-2026-33186) - Fixed a regression in handling the keyword
nullable - Upgrade to
go-1.25.8(CVE-2026-27142, CVE-2026-25679) - Upgrade to
go-grpc 1.79.0
- Upgrade to
42crunch/apifirewall:v1.2.0- Support for the OAS v3.1
- Upgrade to
go-1.25.6(CVE-2025-68121, CVE-2025-61728, CVE-2025-61726, CVE-2025-61731, CVE-2025-68119) - Upgrade to
openssl 3.5.5(CVE-2025-11187, CVE-2025-15467, CVE-2025-15468, CVE-2025-15469, CVE-2025-66199, CVE-2025-68160, CVE-2025-69418, CVE-2025-69419, CVE-2025-69420, CVE-2025-69421, CVE-2026-22795, CVE-2026-22796)
-
42crunch/apifirewall:v1.1.16- Upgrade to
httpd-2.4.66(CVE-2025-55753, CVE-2025-58098, CVE-2025-59775, CVE-2025-65082, CVE-2025-66200) - Upgrade to
golang-1.25.5(CVE-2025-61727, CVE-2025-61729)
- Upgrade to
42crunch/apifirewall:v1.1.15- Upgrade to
PCRE2-10.46(CVE-2025-58050)
- Upgrade to
-
42crunch/apifirewall:v1.1.14- Upgrade to
openssl-3.5.4(CVE-2025-9230, CVE-2025-9231, CVE-2025-9232) - Upgrade to
libexpat-2.7.3(CVE-2025-59375) - Upgrade to
go-1.25.3(CVE-2025-61724, CVE-2025-58187, CVE-2025-47912, CVE-2025-58183, CVE-2025-61723, CVE-2025-58186, CVE-2025-58185, CVE-2025-58188, CVE-2025-61725)
- Upgrade to
42crunch/apifirewall:v1.1.13- Upgrade to
httpd-2.4.65(CVE-2025-53020, CVE-2025-49812, CVE-2025-49630, CVE-2025-23048, CVE-2024-47252, CVE-2024-43394, CVE-2024-43204, CVE-2024-42516, CVE-2025-54090)
- Upgrade to
42crunch/apifirewall:v1.1.12- Fixed handling of schema validating errors
- Upgrade to
go-1.24.4(CVE-2024-45338) - Upgrade to
go-grpc 1.73.0
-
42crunch/apifirewall:v1.1.11- Fixed resource consumption on graceful restart
-
42crunch/apifirewall:v1.1.9- Upgrade to
expat 2.7.0-r0(CVE-2024-8176) - Upgrade to
golang.org/x/net 0.36.0(CVE-2025-22870)
- Upgrade to
42crunch/apifirewall:v1.1.8- Upgrade to
openssl-3.3.3(CVE-2024-12797, CVE-2024-13176)
- Upgrade to
42crunch/apifirewall:v1.1.7- Fixed the failure in forwarding large request bodies
- Upgrade to
go-1.23.4(CVE-2024-45338)
-
42crunch/apifirewall:v1.1.6- Upgrade to
openssl-3.3.2-r1(CVE-2024-9143)
- Upgrade to
42crunch/apifirewall:v1.1.5- Switch to the system certificate store to fix certificate authority renewal issue
All previous image versions have been deprecated and are no longer supported. We highly recommend that you switch to the latest image version to take the full advantage of the new features and security improvements.
When you switch the version of the API Firewall image, you must reconfigure any existing protection configurations so that they work with the new version. For more details, see Reconfigure API Protection.
API Scan images
This release is compatible with the following API Scan images for running it on-premises. The major release number indicates if the image is for Scan v1 or Scan v2 engine.
Scan v2
- NEW:
42crunch/scand-agent:v2.61.0- Upgrade to
Golang 1.27.3(CVE-2026-111943) - Upgrade to
golang.org/x/net v0.62.0(CVE-2026-78661, CVE-2026-97045)
- Upgrade to
We highly recommend that you switch to the latest image version to take full advantage of the new features and security improvements.
42crunch/scand-agent:v2.60.3- Upgrade to
Golang 1.27.2(CVE-2026-56857, CVE-2026-56866, CVE-2026-78659, CVE-2026-78660, CVE-2026-78663, CVE-2026-78667, CVE-2026-78669, CVE-2026-94439, CVE-2026-94440, CVE-2026-94448, CVE-2026-97030, CVE-2026-97031, CVE-2026-97032) - Upgrades to
golang.org/x/crypto v0.58.0andgolang.org/x/net v0.61.0(CVE-2026-56857, CVE-2026-56866, CVE-2026-78659, CVE-2026-78660, CVE-2026-78663, CVE-2026-78667, CVE-2026-78669, CVE-2026-94439, CVE-2026-94440, CVE-2026-94448, CVE-2026-97030, CVE-2026-97031, CVE-2026-97032) - Fixed handling of nullable string properties where the pattern allows for empty strings
- Upgrade to
42crunch/scand-agent:v2.60.1- Multiple expected response codes for any test in a happy path scenario
42crunch/scand-agent:v2.59.2- Upgrades to Go dependencies:
grpc v1.82.1(CVE-2026-84304)golang.org/x/crypto v0.56.0(CVE-2026-56855, CVE-2026-78662)
- Upgrades to Go dependencies:
42crunch/scand-agent:v2.59.0- Upgrade to
Golang 1.26.6(CVE-2026-33818, CVE-2026-39821, CVE-2026-46600, CVE-2026-56853, CVE-2026-56858, CVE-2026-56859, CVE-2026-56860, CVE-2026-56862, CVE-2026-56864, CVE-2026-56865) - Fixed handling of
{{$randomFromSchema}} - Fixed the displayed case of some headers
- Upgrade to
42crunch/scand-agent:v2.58.4- Upgrades to Go dependencies:
grpc v1.82.1(GHSA-hrxh-6v49-42gf)kin-openapi v0.145.0(GHSA-jpcw-4wr7-c3vq, GHSA-r277-6w6q-xmqw)cel-go v0.30.0(GHSA-gcjh-h69q-9w9g)opentelemetry-go v1.44.0(CVE-2026-41178)
- Upgrades to Go dependencies:
42crunch/scand-agent:v2.58.1- Upgrade to
Golang 1.26.5(CVE-2026-39822, CVE-2026-42505) - Support for the constraints
exclusiveMin,exclusiveMax,oneOf, andequalsin GraphQL files - Support for nested queries and
HTTP 413as the expected response code for certain tests in API Scan for GraphQL - Fixed handling of empty arrays in GraphQL files
- Upgrade to
42crunch/scand-agent:v2.57.0- Support for GraphQL federation
- Fixed handling of the format
datewhen generating scan requests
42crunch/scand-agent:v2.56.3- Upgrade to
Golang 1.26.4(CVE-2026-27145, CVE-2026-42504, CVE-2026-42507) - Updated Go dependencies (CVE-2026-39827, CVE-2026-39828, CVE-2026-39829, CVE-2026-39830, CVE-2026-39831, CVE-2026-39832, CVE-2026-39833, CVE-2026-39834, CVE-2026-39835)
- Improved handling of values from
x-42c-samplewhen scanning GraphQL files - Improvements to the handling of path parameters in the test
parameter-required-scan
- Upgrade to
42crunch/scand-agent:v2.56.1- Updated Go dependencies (GHSA-gxhx-2686-5h9g)
- Fixed handling of OpenAPI schemas that have
minimumdefined but notmaximum - Fixed array tests for OpenAPI definitions that have nested arrays with an empty sub array
-
42crunch/scand-agent:v2.56.0- Upgrade to
Golang 1.26.3(CVE-2026-33811, CVE-2026-33814, CVE-2026-39820, CVE-2026-39823, CVE-2026-39825, CVE-2026-39826, CVE-2026-39836, CVE-2026-42499) - Upgrade to
opentelemetry-go 1.43.0(CVE-2026-39883) - Fixed sending of
Content-Typeheaders when testing the content type handling
- Upgrade to
42crunch/scand-agent:v2.55.1- Upgrade to
Golang 1.26.2(CVE-2026-32280, CVE-2026-32281, CVE-2026-32282, CVE-2026-32283, CVE-2026-32288, CVE-2026-32289, CVE-2026-33810) - Fixed running of all scan types
- Upgrade to
42crunch/scand-agent:v2.55.0- Fixed value generation for
oneOfschemas with multiple accepted object types - Fixed handling of empty input objects in GraphQL APIs
- Increased maximum length of returned responses for GraphQL APIs
- Fixed value generation for
42crunch/scand-agent:v2.54.2- Upgrade to
google.golang.org/grpc v1.79.3(CVE-2026-33186) - Improvements to GraphQL support
- Upgrade to
Golang 1.26.1(CVE-2026-25679, CVE-2026-27137, CVE-2026-27138, CVE-2026-27139, CVE-2026-27142)
- Upgrade to
42crunch/scand-agent:v2.53.2- Upgrade to
google.golang.org/grpc v1.79.3(CVE-2026-33186)
- Upgrade to
42crunch/scand-agent:v2.53.1- Fix to scan runtime settings
42crunch/scand-agent:v2.53.0- Fixed value generation on conformance tests
- Upgrade to
Golang 1.25.6(CVE-2025-61726, CVE-2025-61728, CVE-2025-61730)
42crunch/scand-agent:v2.52.0- Upgrade to
golang.org/x/crypto v0.45.0(CVE-2025-47914, CVE-2025-58181)
- Upgrade to
42crunch/scand-agent:v2.51.0- Upgrade to
golang.org/x/crypto v0.44.0(CVE-2025-47913) - Fixed including nested objects in arrays in requests
- Upgrade to
42crunch/scand-agent:v2.50.2- Upgrade to
Golang 1.25.3(CVE-2025-58185) - Adjusted proxy behavior
- Fixed handling of examples in test generation
- Upgrade to
42crunch/scand-agent:v2.50.0- Upgrade to
Golang 1.25.1(CVE-2025-47906) - Fixed generating a value for a test in case of an overflow
- Fixed calculation of estimated tests in case of skipped tests
- Fixed parsing error with long strings of numbers
- Upgrade to
42crunch/scand-agent:v2.49.0- Support for drift scan
42crunch/scand-agent:v2.48.0- Ignore unsupported operations during scan
- Fixed calculation of estimated tests and executed tests
- Fixed variable replacement in Scan v2 in v1-compatible mode
42crunch/scand-agent:v2.47.0- Ignore unsupported methods
X-Scan-Transactionidincluded in every request- Upgrade to
chi v5.2.2(CWE-601)
42crunch/scand-agent:v2.46.3- Upgrade to
Golang 1.24.4(CVE-2025-0913, CVE-2025-22874, CVE-2025-4673)
- Upgrade to
42crunch/scand-agent:v2.46.1- Scan rules defined in the platform taken into account in scans
- URL normalization
42crunch/scand-agent:v2.45.0- Upgrade to
Golang 1.24.2(CVE-2025-22871) - Upgrade to
golang.org/x/net v0.39.0(CVE-2025-22872)
- Upgrade to
All previous image versions have been deprecated and are no longer supported.
Scan v1
- NEW:
42crunch/scand-agent:v1.61.0- Upgrade to
Golang 1.27.3(CVE-2026-111943) - Upgrade to
golang.org/x/net v0.62.0(CVE-2026-78661, CVE-2026-97045)
- Upgrade to
We highly recommend that you switch to the latest image version to take full advantage of the new features and security improvements.
42crunch/scand-agent:v1.60.3- Upgrade to
Golang 1.27.2(CVE-2026-56857, CVE-2026-56866, CVE-2026-78659, CVE-2026-78660, CVE-2026-78663, CVE-2026-78667, CVE-2026-78669, CVE-2026-94439, CVE-2026-94440, CVE-2026-94448, CVE-2026-97030, CVE-2026-97031, CVE-2026-97032) - Upgrades to
golang.org/x/crypto v0.58.0andgolang.org/x/net v0.61.0(CVE-2026-56857, CVE-2026-56866, CVE-2026-78659, CVE-2026-78660, CVE-2026-78663, CVE-2026-78667, CVE-2026-78669, CVE-2026-94439, CVE-2026-94440, CVE-2026-94448, CVE-2026-97030, CVE-2026-97031, CVE-2026-97032)
- Upgrade to
42crunch/scand-agent:v1.60.1- Internal cleanup and refactoring
42crunch/scand-agent:v1.59.2- Upgrades to Go dependencies:
grpc v1.82.1(CVE-2026-84304)golang.org/x/crypto v0.56.0(CVE-2026-56855, CVE-2026-78662)
- Upgrades to Go dependencies:
42crunch/scand-agent:v1.59.0- Upgrade to
Golang 1.26.6(CVE-2026-33818, CVE-2026-39821, CVE-2026-46600, CVE-2026-56853, CVE-2026-56858, CVE-2026-56859, CVE-2026-56860, CVE-2026-56862, CVE-2026-56864, CVE-2026-56865)
- Upgrade to
42crunch/scand-agent:v1.58.4- Upgrades to Go dependencies:
grpc v1.82.1(GHSA-hrxh-6v49-42gf)kin-openapi v0.145.0(GHSA-jpcw-4wr7-c3vq, GHSA-r277-6w6q-xmqw)cel-go v0.30.0(GHSA-gcjh-h69q-9w9g)opentelemetry-go v1.44.0(CVE-2026-41178)
- Upgrades to Go dependencies:
42crunch/scand-agent:v1.58.1- Upgrade to
Golang 1.26.5(CVE-2026-39822, CVE-2026-42505)
- Upgrade to
42crunch/scand-agent:v1.57.0- Internal cleanup and refactoring
42crunch/scand-agent:v1.56.3- Upgrade to
Golang 1.26.4(CVE-2026-27145, CVE-2026-42504, CVE-2026-42507) - Updated Go dependencies (CVE-2026-39827, CVE-2026-39828, CVE-2026-39829, CVE-2026-39830, CVE-2026-39831, CVE-2026-39832, CVE-2026-39833, CVE-2026-39834, CVE-2026-39835)
- Upgrade to
42crunch/scand-agent:v1.56.1- Updated Go dependencies (GHSA-gxhx-2686-5h9g)
42crunch/scand-agent:v1.56.0- Upgrade to
Golang 1.26.3(CVE-2026-33811, CVE-2026-33814, CVE-2026-39820, CVE-2026-39823, CVE-2026-39825, CVE-2026-39826, CVE-2026-39836, CVE-2026-42499) - Upgrade to
opentelemetry-go 1.43.0(CVE-2026-39883) - Fixed sending of
Content-Typeheaders when testing the content type handling
- Upgrade to
-
42crunch/scand-agent:v1.55.1- Upgrade to
Golang 1.26.2(CVE-2026-32280, CVE-2026-32281, CVE-2026-32282, CVE-2026-32283, CVE-2026-32288, CVE-2026-32289, CVE-2026-33810)
- Upgrade to
-
42crunch/scand-agent:v1.55.0- Internal cleanup and refactoring
42crunch/scand-agent:v1.54.2- Upgrade to
google.golang.org/grpc v1.79.3(CVE-2026-33186) - Upgrade to
Golang 1.26.1(CVE-2026-25679, CVE-2026-27137, CVE-2026-27138, CVE-2026-27139, CVE-2026-27142)
- Upgrade to
42crunch/scand-agent:v1.53.2- Upgrade to
google.golang.org/grpc v1.79.3(CVE-2026-33186)
- Upgrade to
42crunch/scand-agent:v1.53.1- Fix to scan runtime settings
42crunch/scand-agent:v1.53.0- Upgrade to
Golang 1.25.6(CVE-2025-61726, CVE-2025-61728, CVE-2025-61730)
- Upgrade to
-
42crunch/scand-agent:v1.52.0- Upgrade to
golang.org/x/crypto v0.45.0(CVE-2025-47914, CVE-2025-58181)
- Upgrade to
42crunch/scand-agent:v1.51.0- Upgrade to
golang.org/x/crypto v0.44.0(CVE-2025-47913) - Fixed including nested objects in arrays in requests
- Upgrade to
-
42crunch/scand-agent:v1.50.2- Upgrade to
Golang 1.25.3(CVE-2025-58185) - Adjusted proxy behavior
- Upgrade to
42crunch/scand-agent:v1.50.0- Upgrade to
Golang 1.25.1(CVE-2025-47906)
- Upgrade to
42crunch/scand-agent:v1.49.0- Internal cleanup and refactoring
42crunch/scand-agent:v1.48.0- Fixed scan report size checks
42crunch/scand-agent:v1.47.0- Ignore unsupported HTTP methods
X-Scan-Transactionidincluded in every request- Upgrade to
chi v5.2.2(CWE-601)
-
42crunch/scand-agent:v1.46.3- Upgrade to
Golang 1.24.4(CVE-2025-0913, CVE-2025-22874, CVE-2025-4673)
- Upgrade to
42crunch/scand-agent:v1.46.0- Internal cleanup and refactoring
42crunch/scand-agent:v1.45.0- Upgrade to
Golang 1.24.2(CVE-2025-22871) - Upgrade to
golang.org/x/net v0.39.0(CVE-2025-22872)
- Upgrade to
All previous image versions have been deprecated and are no longer supported.
Changed behavior
- Depending on your API, the improved support for the OAS v3.1.x for JSON keywords may mean that it no longer has semantic issues and is deemed a valid OpenAPI definition.
- The changes to the scoring algorithm can affect the audit scores of your GraphQL data definition files.
Deprecated components
The following have been deprecated and will be removed in the future.
There are no new deprecations in this release. For the list of current deprecations, see List of deprecated images and endpoints.
Known issues
This release has the following known issues.
Some permissions not shown on list of users
The permissions for managing teams, creating API collections, or importing new APIs to 42Crunch Platform are not yet shown on the list of users in your organization. However, you can view all permissions that a user has by clicking the permission column. This permissions also do not yet have a shortcut that you could use when searching by permission.
These will be fixed in a future release.
Changing tagging on an API may trigger an unrelated error on the UI
Sometimes applying tags to or removing them from an API may trigger an unrelated error on failing to fetch the SQG approval report for the API. This happens if the API in question has been scanned on-premises and the scan has finished after you arrived on the API Summary page, because the UI cannot find the latest on-premises scan report and the associated approval report. Refreshing the page gets the latest reports and resolves the issue.
Tagging and untagging the API is not affected by this error: tags get correctly applied and removed in any case.
This will be fixed in a future release.
Data dictionary duplication
Duplicating a data dictionary does not yet duplicate the values in it.
This will be fixed in a future release.
Scan customization rules may lead to no response codes being accepted.
In some cases, scan rules can lead to HTTP status response codes in API responses that are normally expected (for example, HTTP 401 or HTTP 404) to be treated as unexpected. This in turn can lead to a false positive in the scan results.
By default, the expected HTTP status response codes that are defined in scan rules applied to the scanned API take preference over the response codes that API Scan would otherwise expect. However, this can cause problems in scan process if your scan rule only skips header or response body analysis but does not define any expected response codes, either for happy path requests or for particular test IDs. This results in the scan rule to have null defined as the expected response code, and because the scan rule takes preference over the default scan behavior, no response codes except null are accepted. This in turn means that some tests are incorrectly flagged as returning unexpected response codes when they were in fact successful.
We are currently investigating the best way how to reconcile the designed behavior of API Scan and scan rules in these cases, and this issue will be fixed in a future release.