42Crunch Platform release, September 30, 2026
|
Platform version: v1.60.x |
This 42Crunch API Security Platform release introduces a preview of MCP Security Governance in 42Crunch Platform.
New features
The following are the new features and improvements to the existing ones in this release.
MCP Security Governance in 42Crunch Platform
We have introduced a preview of our 42Crunch MCP Security Governance features as a new, separate part of 42Crunch Platform. MCP (Model Context Protocol) is a standard for connecting AI applications and agents to external systems: the AI application uses MCP clients to establish connections to one or more MCP servers to access resources and tools that the AI application needs for accomplishing the task it has been given.
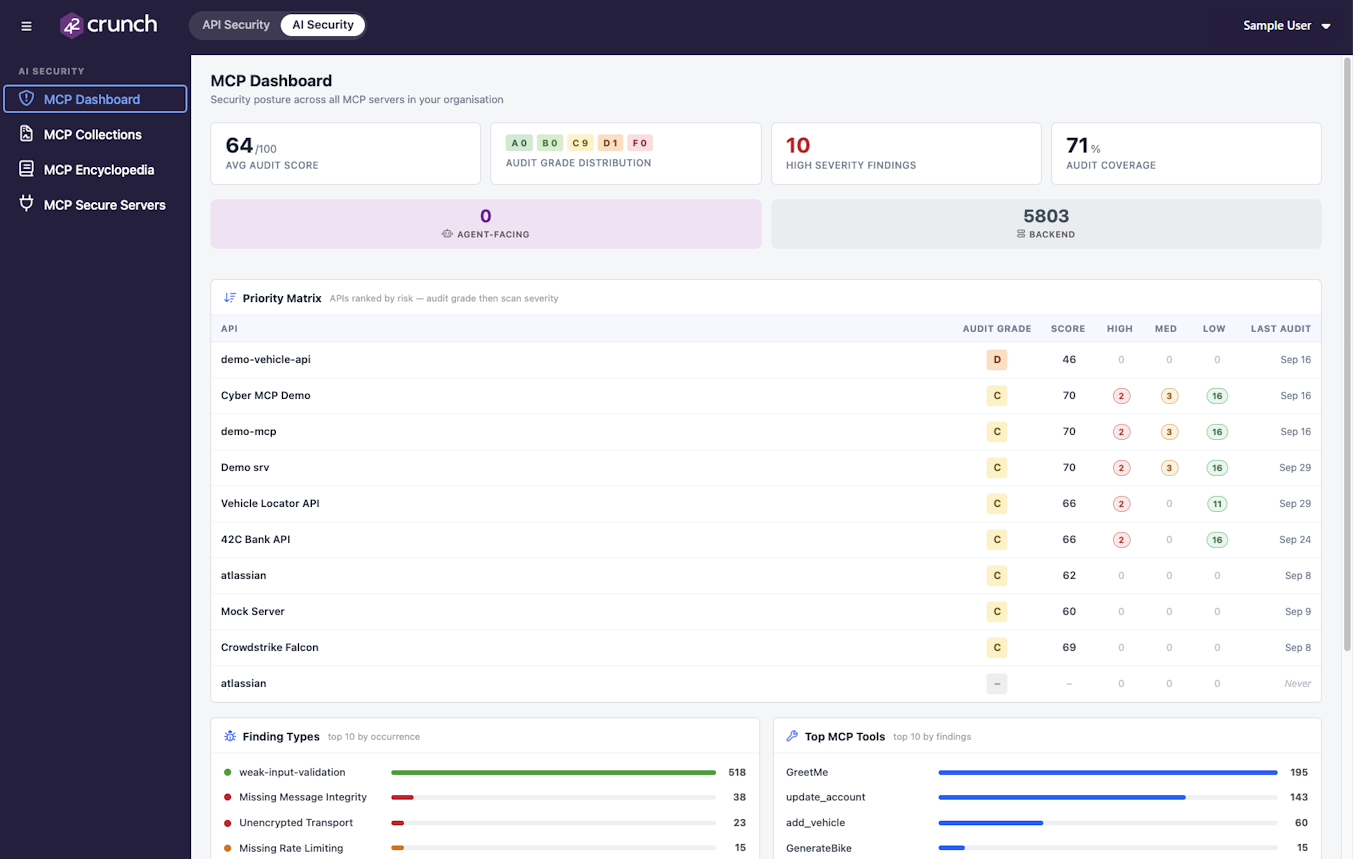
MCP Security Governance gives enterprises detailed AI exposure management across every MCP server they run or consume and detailed reporting on their compliance with the AI regulatory frameworks that apply to them.
- Automatically discover and document any HTTP MCP server (live within your organization or at an external third party) from its exposition URL
- Assess the security of the discovered MCP servers to surface and address the risks found in them
- Actively scan the MCP server to verify that authentication and authorization are properly in place, and that malformed, defective, or anomalous payloads are properly rejected
- Generate compliance reports against the major regulatory frameworks, such as NIST AI-RMF, EU AI Act, ISO 42001, and CSA-AICM
- Generate MCP server status report against OWASP MCP Top 10
Support for MCP Security Governance is not enabled by default, but is available as a separate subscription. If you are interested in adding MCP security governance to your subscription, contact sales@42crunch.com.
More granularity to audit security quality gates for OpenAPI definitions
The security quality gates (SQGs) for API Security Audit let you reject OpenAPI definitions that are not valid according to the requirements of the OpenAPI Specification (OAS). Previously, this meant that both structural and semantic issues caused an API to fail the SQG, but now you can also choose to reject only on structural issues, letting APIs with only semantic issues through.
This does not mean that semantic issues can be ignored: an API which semantically does not meet the requirements of the OAS is still not a fully valid OpenAPI definition. You cannot deploy API Protection for an OpenAPI definition with semantic issues, and they may cause problems with API Scan, so the semantic issues must eventually be fixed so that your API definition can be consumed properly an unambiguously.
However, there may be cases where treating semantic issues initially more leniently than structural errors makes sense. For example, if you have integrated 42Crunch Platform with your CI/CD pipelines so that the SQGs are blocking APIs from entering the codebase, which might prevent other teams from integrating with them, slowing down your development. In this case, allowing the semantic issues through could allow the wider development to start already while you are fixing the semantic issues.
For more details, see Security quality gates.
Improvements to the Scan v2
We have done several smaller improvements to Scan v2:
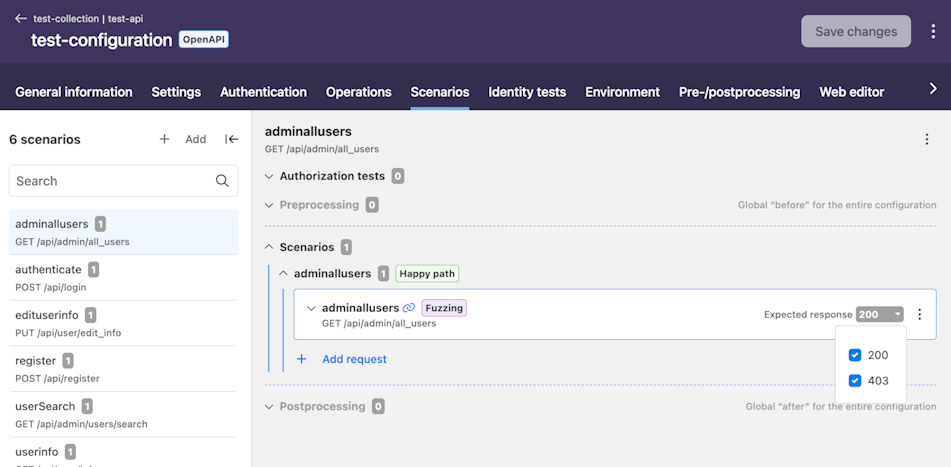
- You can now define multiple expected response codes when configuring the details for requests in scan scenarios.
- The parsing of large scan reports on the platform UI has been fixed, so that all issues in the report are correctly rendered on the UI.
- The scan report now clearly shows skipped tests as having been skipped, not failed.
- We have clarified wordings in the scan configuration validation report (SCVR).
Bulk deletion of user accounts
Organization administrators can now delete multiple user accounts in their organization at one go, for example, to clean up stale accounts you have accumulated in 42Crunch Platform. Simply tick the boxes for the users you want to delete and then click the Delete button above the list.
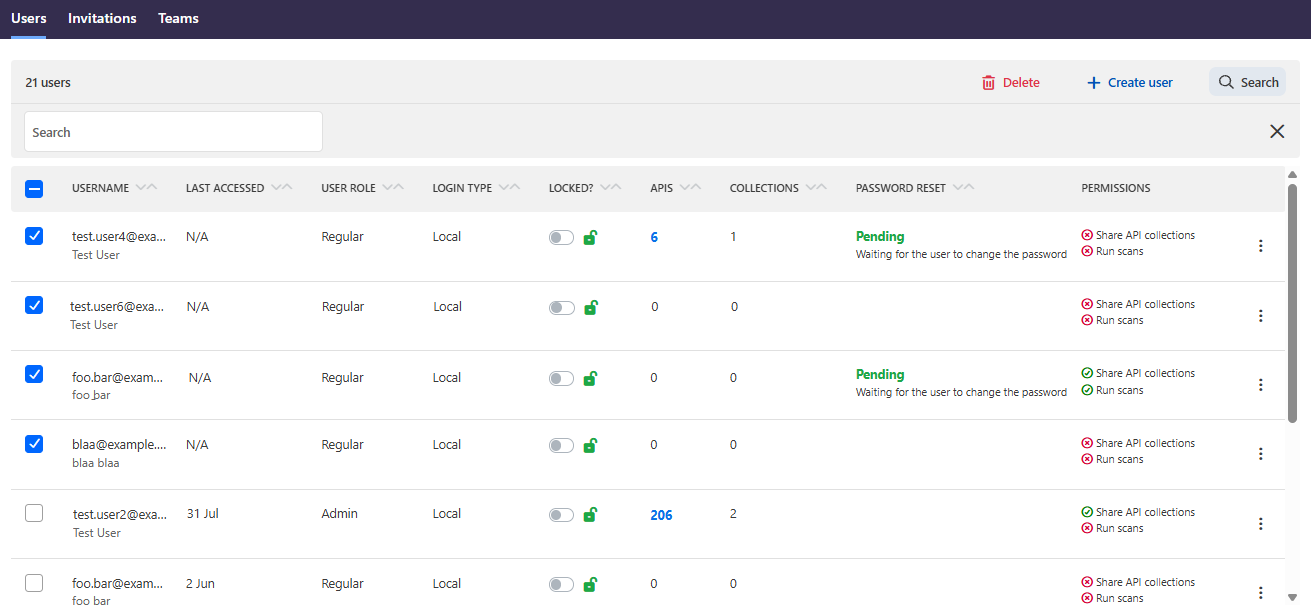
To avoid losing any assets that the selected accounts may own, you must choose a new owner for them. The same owner will receive the assets from all accounts that you are deleting. If some of the user accounts cannot be deleted, you will be notified about those and can still proceed to delete the rest of the selected user accounts.
For more details, see Users and organizations.
Improvements to GraphQL support
Data definition files now also get a proper audit score and you can enforce minimum score in the SQG criteria. The grading algorithm in Security Audit takes into account that the direction of the traffic might not always be known on data definition files, and so the same issue might have a different impact in a schema definition file and in a data definition file. For more details. see Auditing GraphQL data definition files.
In addition, we have fixed the following:
- The GraphQL scan configuration page now shows the targeted API endpoint URL, just like with OpenAPI definitions.
- We have improved the support of input arguments in the nested fields of returned objects in API Scan.
- The fingerprint in GraphQL scan reports were not always correctly processed, leading to confusing behavior when viewing the issue details on the platform UI. This has now been fixed.
Support for GraphQL is not enabled by default, but is available as a separate subscription. If you are interested in adding GraphQL support to your subscription, contact sales@42crunch.com.
GraphQL is not yet supported in API Protection, CI/CD plugins, data dictionaries, or API Contract Generator.
Other improvements
We have improved the support for browser multitasking features: for example, if working on customization rules or security quality gates, you can now easily right-click and open the tag list to a split view or onto another tab so that you do not have to navigate back and forth.
Compatibility
This section lists the compatible Docker images for some of the components of 42Crunch API Security Platform, as well as other possible compatibility details.
API Firewall images
This release is compatible with the following API Firewall images:
- NEW:
42crunch/apifirewall:v1.2.11- Upgrade to
go-grpc-1.83.1(CVE-2026-84303, CVE-2026-84304, CVE-2026-84445) - Upgrade to
openssl-3.5.8CVE-2026-14456, CVE-2026-14457, CVE-2026-18798, CVE-2026-54874, CVE-2026-63072, CVE-2026-63073, CVE-2026-63074, CVE-2026-63075, CVE-2026-63076, CVE-2026-75803) - Upgrade to
util-linux 2.42.3(CVE-2026-76642, CVE-2026-78408, CVE-2026-78409, CVE-2026-78410) - Upgrade to
expat-2.8.4(CVE-2026-66046, CVE-2026-76641, CVE-2026-76956, CVE-2026-76957) - Upgrade to
pcre2-10.48(CVE-2026-89157, CVE-2026-89160, CVE-2026-89162)
- Upgrade to
We highly recommend that you switch to the latest image version to take full advantage of the new features and security improvements.
42crunch/apifirewall:v1.2.10- Upgrade to
go-1.26.6(CVE-2026-33818, CVE-2026-56853, CVE-2026-56858, CVE-2026-56859, CVE-2026-56860, CVE-2026-56862, CVE-2026-56864, CVE-2026-568652) - Upgrade to
apr-util-1.6.5(CVE-2025-49506, CVE-2026-32327, CVE-2026-341) - Upgrade to
memcached-1.6.45(CVE-2026-47783, CVE-2026-47784)
- Upgrade to
42crunch/apifirewall:v1.2.9- Upgrade to
go-grpc-1.82.1(GHSA-hrxh-6v49-42gf) - Upgrade to
go-1.26.5(CVE-2026-39822) - Upgrade to
expat-2.8.2(CVE-2026-50219)
- Upgrade to
42crunch/apifirewall:v1.2.7- Upgrade to
openssl-3.5.7(CVE-2026-34180, CVE-2026-34181, CVE-2026-34182, CVE-2026-34183, CVE-2026-35188, CVE-2026-42764, CVE-2026-42765, CVE-2026-42766, CVE-2026-42767, CVE-2026-42768, CVE-2026-42769, CVE-2026-42770, CVE-2026-45445, CVE-2026-45446, CVE-2026-45447, CVE-2026-7383, CVE-2026-9076)
- Upgrade to
42crunch/apifirewall:v1.2.6- Fix loading some OpenAPI definitions that failed with an error on unresolved reference
- Upgrade to
httpd-2.4.68(CVE-2026-29167, CVE-2026-29170, CVE-2026-34355, CVE-2026-34356, CVE-2026-42535, CVE-2026-42536, CVE-2026-43951, CVE-2026-44119, CVE-2026-44185, CVE-2026-44186, CVE-2026-44631, CVE-2026-48913, CVE-2026-49975) - Upgrade to
golang-1.26.4(CVE-2026-27145, CVE-2026-42504, CVE-2026-42507) - Upgrade to
go-net v0.55.0(CVE-2026-39821)
42crunch/apifirewall:v1.2.4- Upgrade to
golang-1.26.3(CVE-2026-32283, CVE-2026-32282, CVE-2026-27144, CVE-2026-27140, CVE-2026-27143, CVE-2026-33810, CVE-2026-32289, CVE-2026-32288, CVE-2026-42501, CVE-2026-27142, CVE-2026-39836) - Upgrade to
openssl-3.5.6(CVE-2026-31789, CVE-2026-28387, CVE-2026-40200, CVE-2026-2673) - Upgrade to
httpd-2.4.67(CVE-2026-23918, CVE-2026-24072, CVE-2026-28780, CVE-2026-29168, CVE-2026-29169, CVE-2026-33006, CVE-2026-33007, CVE-2026-33523, CVE-2026-33857, CVE-2026-34032, CVE-2026-34059)
- Upgrade to
42crunch/apifirewall:v1.2.3- Upgrade to
go-1.26.1
- Upgrade to
-
42crunch/apifirewall:v1.2.2- Upgrade to
go-grpc 1.79.3(CVE-2026-33186) - Fixed a regression in handling the keyword
nullable - Upgrade to
go-1.25.8(CVE-2026-27142, CVE-2026-25679) - Upgrade to
go-grpc 1.79.0
- Upgrade to
42crunch/apifirewall:v1.2.0- Support for the OAS v3.1
- Upgrade to
go-1.25.6(CVE-2025-68121, CVE-2025-61728, CVE-2025-61726, CVE-2025-61731, CVE-2025-68119) - Upgrade to
openssl 3.5.5(CVE-2025-11187, CVE-2025-15467, CVE-2025-15468, CVE-2025-15469, CVE-2025-66199, CVE-2025-68160, CVE-2025-69418, CVE-2025-69419, CVE-2025-69420, CVE-2025-69421, CVE-2026-22795, CVE-2026-22796)
-
42crunch/apifirewall:v1.1.16- Upgrade to
httpd-2.4.66(CVE-2025-55753, CVE-2025-58098, CVE-2025-59775, CVE-2025-65082, CVE-2025-66200) - Upgrade to
golang-1.25.5(CVE-2025-61727, CVE-2025-61729)
- Upgrade to
42crunch/apifirewall:v1.1.15- Upgrade to
PCRE2-10.46(CVE-2025-58050)
- Upgrade to
-
42crunch/apifirewall:v1.1.14- Upgrade to
openssl-3.5.4(CVE-2025-9230, CVE-2025-9231, CVE-2025-9232) - Upgrade to
libexpat-2.7.3(CVE-2025-59375) - Upgrade to
go-1.25.3(CVE-2025-61724, CVE-2025-58187, CVE-2025-47912, CVE-2025-58183, CVE-2025-61723, CVE-2025-58186, CVE-2025-58185, CVE-2025-58188, CVE-2025-61725)
- Upgrade to
42crunch/apifirewall:v1.1.13- Upgrade to
httpd-2.4.65(CVE-2025-53020, CVE-2025-49812, CVE-2025-49630, CVE-2025-23048, CVE-2024-47252, CVE-2024-43394, CVE-2024-43204, CVE-2024-42516, CVE-2025-54090)
- Upgrade to
42crunch/apifirewall:v1.1.12- Fixed handling of schema validating errors
- Upgrade to
go-1.24.4(CVE-2024-45338) - Upgrade to
go-grpc 1.73.0
-
42crunch/apifirewall:v1.1.11- Fixed resource consumption on graceful restart
-
42crunch/apifirewall:v1.1.9- Upgrade to
expat 2.7.0-r0(CVE-2024-8176) - Upgrade to
golang.org/x/net 0.36.0(CVE-2025-22870)
- Upgrade to
42crunch/apifirewall:v1.1.8- Upgrade to
openssl-3.3.3(CVE-2024-12797, CVE-2024-13176)
- Upgrade to
42crunch/apifirewall:v1.1.7- Fixed the failure in forwarding large request bodies
- Upgrade to
go-1.23.4(CVE-2024-45338)
-
42crunch/apifirewall:v1.1.6- Upgrade to
openssl-3.3.2-r1(CVE-2024-9143)
- Upgrade to
42crunch/apifirewall:v1.1.5- Switch to the system certificate store to fix certificate authority renewal issue
All previous image versions have been deprecated and are no longer supported. We highly recommend that you switch to the latest image version to take the full advantage of the new features and security improvements.
When you switch the version of the API Firewall image, you must reconfigure any existing protection configurations so that they work with the new version. For more details, see Reconfigure API Protection.
API Scan images
This release is compatible with the following API Scan images for running it on-premises. The major release number indicates if the image is for Scan v1 or Scan v2 engine.
Scan v2
- NEW:
42crunch/scand-agent:v2.60.1- Multiple expected response codes for any test in a happy path scenario
We highly recommend that you switch to the latest image version to take full advantage of the new features and security improvements.
42crunch/scand-agent:v2.59.2- Upgrades to Go dependencies:
grpc v1.82.1(CVE-2026-84304)golang.org/x/crypto v0.56.0(CVE-2026-56855, CVE-2026-78662)
- Upgrades to Go dependencies:
42crunch/scand-agent:v2.59.0- Upgrade to
Golang 1.26.6(CVE-2026-33818, CVE-2026-39821, CVE-2026-46600, CVE-2026-56853, CVE-2026-56858, CVE-2026-56859, CVE-2026-56860, CVE-2026-56862, CVE-2026-56864, CVE-2026-56865) - Fixed handling of
{{$randomFromSchema}} - Fixed the displayed case of some headers
- Upgrade to
42crunch/scand-agent:v2.58.4- Upgrades to Go dependencies:
grpc v1.82.1(GHSA-hrxh-6v49-42gf)kin-openapi v0.145.0(GHSA-jpcw-4wr7-c3vq, GHSA-r277-6w6q-xmqw)cel-go v0.30.0(GHSA-gcjh-h69q-9w9g)opentelemetry-go v1.44.0(CVE-2026-41178)
- Upgrades to Go dependencies:
42crunch/scand-agent:v2.58.1- Upgrade to
Golang 1.26.5(CVE-2026-39822, CVE-2026-42505) - Support for the constraints
exclusiveMin,exclusiveMax,oneOf, andequalsin GraphQL files - Support for nested queries and
HTTP 413as the expected response code for certain tests in API Scan for GraphQL - Fixed handling of empty arrays in GraphQL files
- Upgrade to
42crunch/scand-agent:v2.57.0- Support for GraphQL federation
- Fixed handling of the format
datewhen generating scan requests
42crunch/scand-agent:v2.56.3- Upgrade to
Golang 1.26.4(CVE-2026-27145, CVE-2026-42504, CVE-2026-42507) - Updated Go dependencies (CVE-2026-39827, CVE-2026-39828, CVE-2026-39829, CVE-2026-39830, CVE-2026-39831, CVE-2026-39832, CVE-2026-39833, CVE-2026-39834, CVE-2026-39835)
- Improved handling of values from
x-42c-samplewhen scanning GraphQL files - Improvements to the handling of path parameters in the test
parameter-required-scan
- Upgrade to
42crunch/scand-agent:v2.56.1- Updated Go dependencies (GHSA-gxhx-2686-5h9g)
- Fixed handling of OpenAPI schemas that have
minimumdefined but notmaximum - Fixed array tests for OpenAPI definitions that have nested arrays with an empty sub array
-
42crunch/scand-agent:v2.56.0- Upgrade to
Golang 1.26.3(CVE-2026-33811, CVE-2026-33814, CVE-2026-39820, CVE-2026-39823, CVE-2026-39825, CVE-2026-39826, CVE-2026-39836, CVE-2026-42499) - Upgrade to
opentelemetry-go 1.43.0(CVE-2026-39883) - Fixed sending of
Content-Typeheaders when testing the content type handling
- Upgrade to
42crunch/scand-agent:v2.55.1- Upgrade to
Golang 1.26.2(CVE-2026-32280, CVE-2026-32281, CVE-2026-32282, CVE-2026-32283, CVE-2026-32288, CVE-2026-32289, CVE-2026-33810) - Fixed running of all scan types
- Upgrade to
42crunch/scand-agent:v2.55.0- Fixed value generation for
oneOfschemas with multiple accepted object types - Fixed handling of empty input objects in GraphQL APIs
- Increased maximum length of returned responses for GraphQL APIs
- Fixed value generation for
42crunch/scand-agent:v2.54.2- Upgrade to
google.golang.org/grpc v1.79.3(CVE-2026-33186) - Improvements to GraphQL support
- Upgrade to
Golang 1.26.1(CVE-2026-25679, CVE-2026-27137, CVE-2026-27138, CVE-2026-27139, CVE-2026-27142)
- Upgrade to
42crunch/scand-agent:v2.53.2- Upgrade to
google.golang.org/grpc v1.79.3(CVE-2026-33186)
- Upgrade to
42crunch/scand-agent:v2.53.1- Fix to scan runtime settings
42crunch/scand-agent:v2.53.0- Fixed value generation on conformance tests
- Upgrade to
Golang 1.25.6(CVE-2025-61726, CVE-2025-61728, CVE-2025-61730)
42crunch/scand-agent:v2.52.0- Upgrade to
golang.org/x/crypto v0.45.0(CVE-2025-47914, CVE-2025-58181)
- Upgrade to
42crunch/scand-agent:v2.51.0- Upgrade to
golang.org/x/crypto v0.44.0(CVE-2025-47913) - Fixed including nested objects in arrays in requests
- Upgrade to
42crunch/scand-agent:v2.50.2- Upgrade to
Golang 1.25.3(CVE-2025-58185) - Adjusted proxy behavior
- Fixed handling of examples in test generation
- Upgrade to
42crunch/scand-agent:v2.50.0- Upgrade to
Golang 1.25.1(CVE-2025-47906) - Fixed generating a value for a test in case of an overflow
- Fixed calculation of estimated tests in case of skipped tests
- Fixed parsing error with long strings of numbers
- Upgrade to
42crunch/scand-agent:v2.49.0- Support for drift scan
42crunch/scand-agent:v2.48.0- Ignore unsupported operations during scan
- Fixed calculation of estimated tests and executed tests
- Fixed variable replacement in Scan v2 in v1-compatible mode
42crunch/scand-agent:v2.47.0- Ignore unsupported methods
X-Scan-Transactionidincluded in every request- Upgrade to
chi v5.2.2(CWE-601)
42crunch/scand-agent:v2.46.3- Upgrade to
Golang 1.24.4(CVE-2025-0913, CVE-2025-22874, CVE-2025-4673)
- Upgrade to
42crunch/scand-agent:v2.46.1- Scan rules defined in the platform taken into account in scans
- URL normalization
42crunch/scand-agent:v2.45.0- Upgrade to
Golang 1.24.2(CVE-2025-22871) - Upgrade to
golang.org/x/net v0.39.0(CVE-2025-22872)
- Upgrade to
All previous image versions have been deprecated and are no longer supported.
Scan v1
- NEW:
42crunch/scand-agent:v1.60.1- Internal cleanup and refactoring
We highly recommend that you switch to the latest image version to take full advantage of the new features and security improvements.
42crunch/scand-agent:v1.59.2- Upgrades to Go dependencies:
grpc v1.82.1(CVE-2026-84304)golang.org/x/crypto v0.56.0(CVE-2026-56855, CVE-2026-78662)
- Upgrades to Go dependencies:
42crunch/scand-agent:v1.59.0- Upgrade to
Golang 1.26.6(CVE-2026-33818, CVE-2026-39821, CVE-2026-46600, CVE-2026-56853, CVE-2026-56858, CVE-2026-56859, CVE-2026-56860, CVE-2026-56862, CVE-2026-56864, CVE-2026-56865)
- Upgrade to
42crunch/scand-agent:v1.58.4- Upgrades to Go dependencies:
grpc v1.82.1(GHSA-hrxh-6v49-42gf)kin-openapi v0.145.0(GHSA-jpcw-4wr7-c3vq, GHSA-r277-6w6q-xmqw)cel-go v0.30.0(GHSA-gcjh-h69q-9w9g)opentelemetry-go v1.44.0(CVE-2026-41178)
- Upgrades to Go dependencies:
42crunch/scand-agent:v1.58.1- Upgrade to
Golang 1.26.5(CVE-2026-39822, CVE-2026-42505)
- Upgrade to
42crunch/scand-agent:v1.57.0- Internal cleanup and refactoring
42crunch/scand-agent:v1.56.3- Upgrade to
Golang 1.26.4(CVE-2026-27145, CVE-2026-42504, CVE-2026-42507) - Updated Go dependencies (CVE-2026-39827, CVE-2026-39828, CVE-2026-39829, CVE-2026-39830, CVE-2026-39831, CVE-2026-39832, CVE-2026-39833, CVE-2026-39834, CVE-2026-39835)
- Upgrade to
42crunch/scand-agent:v1.56.1- Updated Go dependencies (GHSA-gxhx-2686-5h9g)
42crunch/scand-agent:v1.56.0- Upgrade to
Golang 1.26.3(CVE-2026-33811, CVE-2026-33814, CVE-2026-39820, CVE-2026-39823, CVE-2026-39825, CVE-2026-39826, CVE-2026-39836, CVE-2026-42499) - Upgrade to
opentelemetry-go 1.43.0(CVE-2026-39883) - Fixed sending of
Content-Typeheaders when testing the content type handling
- Upgrade to
-
42crunch/scand-agent:v1.55.1- Upgrade to
Golang 1.26.2(CVE-2026-32280, CVE-2026-32281, CVE-2026-32282, CVE-2026-32283, CVE-2026-32288, CVE-2026-32289, CVE-2026-33810)
- Upgrade to
-
42crunch/scand-agent:v1.55.0- Internal cleanup and refactoring
42crunch/scand-agent:v1.54.2- Upgrade to
google.golang.org/grpc v1.79.3(CVE-2026-33186) - Upgrade to
Golang 1.26.1(CVE-2026-25679, CVE-2026-27137, CVE-2026-27138, CVE-2026-27139, CVE-2026-27142)
- Upgrade to
42crunch/scand-agent:v1.53.2- Upgrade to
google.golang.org/grpc v1.79.3(CVE-2026-33186)
- Upgrade to
42crunch/scand-agent:v1.53.1- Fix to scan runtime settings
42crunch/scand-agent:v1.53.0- Upgrade to
Golang 1.25.6(CVE-2025-61726, CVE-2025-61728, CVE-2025-61730)
- Upgrade to
-
42crunch/scand-agent:v1.52.0- Upgrade to
golang.org/x/crypto v0.45.0(CVE-2025-47914, CVE-2025-58181)
- Upgrade to
42crunch/scand-agent:v1.51.0- Upgrade to
golang.org/x/crypto v0.44.0(CVE-2025-47913) - Fixed including nested objects in arrays in requests
- Upgrade to
-
42crunch/scand-agent:v1.50.2- Upgrade to
Golang 1.25.3(CVE-2025-58185) - Adjusted proxy behavior
- Upgrade to
42crunch/scand-agent:v1.50.0- Upgrade to
Golang 1.25.1(CVE-2025-47906)
- Upgrade to
42crunch/scand-agent:v1.49.0- Internal cleanup and refactoring
42crunch/scand-agent:v1.48.0- Fixed scan report size checks
42crunch/scand-agent:v1.47.0- Ignore unsupported HTTP methods
X-Scan-Transactionidincluded in every request- Upgrade to
chi v5.2.2(CWE-601)
-
42crunch/scand-agent:v1.46.3- Upgrade to
Golang 1.24.4(CVE-2025-0913, CVE-2025-22874, CVE-2025-4673)
- Upgrade to
42crunch/scand-agent:v1.46.0- Internal cleanup and refactoring
42crunch/scand-agent:v1.45.0- Upgrade to
Golang 1.24.2(CVE-2025-22871) - Upgrade to
golang.org/x/net v0.39.0(CVE-2025-22872)
- Upgrade to
All previous image versions have been deprecated and are no longer supported.
Changed behavior
- Regular users who do not have a permission to create new API collections or import APIs must use 42Crunch API Security Testing as the runtime for both audits and scans in their IDEs and have the API definition they are working on stored locally on their device, otherwise the IDE integration does not work.
- Depending on your API, the new checks for Security Audit may increase the number of issues reported on your OpenAPI definition. The validity of the API definition or the audit score do not change.
Deprecated components
The following have been deprecated and will be removed in the future.
There are no new deprecations in this release. For the list of current deprecations, see List of deprecated images and endpoints.
Known issues
This release has the following known issues.
Some permissions not shown on list of users
The permissions for managing teams, creating API collections, or importing new APIs to 42Crunch Platform are not yet shown on the list of users in your organization. However, you can view all permissions that a user has by clicking the permission column. This permissions also do not yet have a shortcut that you could use when searching by permission.
These will be fixed in a future release.
Changing tagging on an API may trigger an unrelated error on the UI
Sometimes applying tags to or removing them from an API may trigger an unrelated error on failing to fetch the SQG approval report for the API. This happens if the API in question has been scanned on-premises and the scan has finished after you arrived on the API Summary page, because the UI cannot find the latest on-premises scan report and the associated approval report. Refreshing the page gets the latest reports and resolves the issue.
Tagging and untagging the API is not affected by this error: tags get correctly applied and removed in any case.
This will be fixed in a future release.
Data dictionary duplication
Duplicating a data dictionary does not yet duplicate the values in it.
This will be fixed in a future release.
Scan customization rules may lead to no response codes being accepted.
In some cases, scan rules can lead to HTTP status response codes in API responses that are normally expected (for example, HTTP 401 or HTTP 404) to be treated as unexpected. This in turn can lead to a false positive in the scan results.
By default, the expected HTTP status response codes that are defined in scan rules applied to the scanned API take preference over the response codes that API Scan would otherwise expect. However, this can cause problems in scan process if your scan rule only skips header or response body analysis but does not define any expected response codes, either for happy path requests or for particular test IDs. This results in the scan rule to have null defined as the expected response code, and because the scan rule takes preference over the default scan behavior, no response codes except null are accepted. This in turn means that some tests are incorrectly flagged as returning unexpected response codes when they were in fact successful.
We are currently investigating the best way how to reconcile the designed behavior of API Scan and scan rules in these cases, and this issue will be fixed in a future release.